
Make talent quality your leading analytic with skills-based hiring solution.
A bug bounty hunter finds security flaws in software before attackers do, proves they’re real, and writes them up so engineers can fix them. A good bug bounty hunter job description tells candidates which systems they’ll test, what kind of findings matter to you, and how you’ll judge their reports, so strong researchers apply and casual scanner users don’t.
The role is sometimes searched as “bag hunter” (a common misspelling of bug hunter), but the work is the same: structured, permission based hunting for vulnerabilities. This page gives you a copy ready template, a breakdown of the role, and a short guide to checking a candidate’s skill before they reach your security lead’s calendar.
A bug bounty hunter is a security researcher who tests applications, APIs, and infrastructure for vulnerabilities such as cross site scripting, SQL injection, broken access control, and server side request forgery. They report each finding with clear reproduction steps, a proof of concept, and a severity rating. Employers hire them full time to run an internal bug bounty program, to triage reports from outside researchers, or to act as an in house offensive tester.
Most bug bounty hunters started as independent researchers, earning rewards from public programs on platforms such as HackerOne or Bugcrowd. When a company hires one as an employee, the job shifts. The hunter still looks for vulnerabilities, but they also own the quality of what gets reported, how fast it gets fixed, and whether the same class of bug keeps coming back.
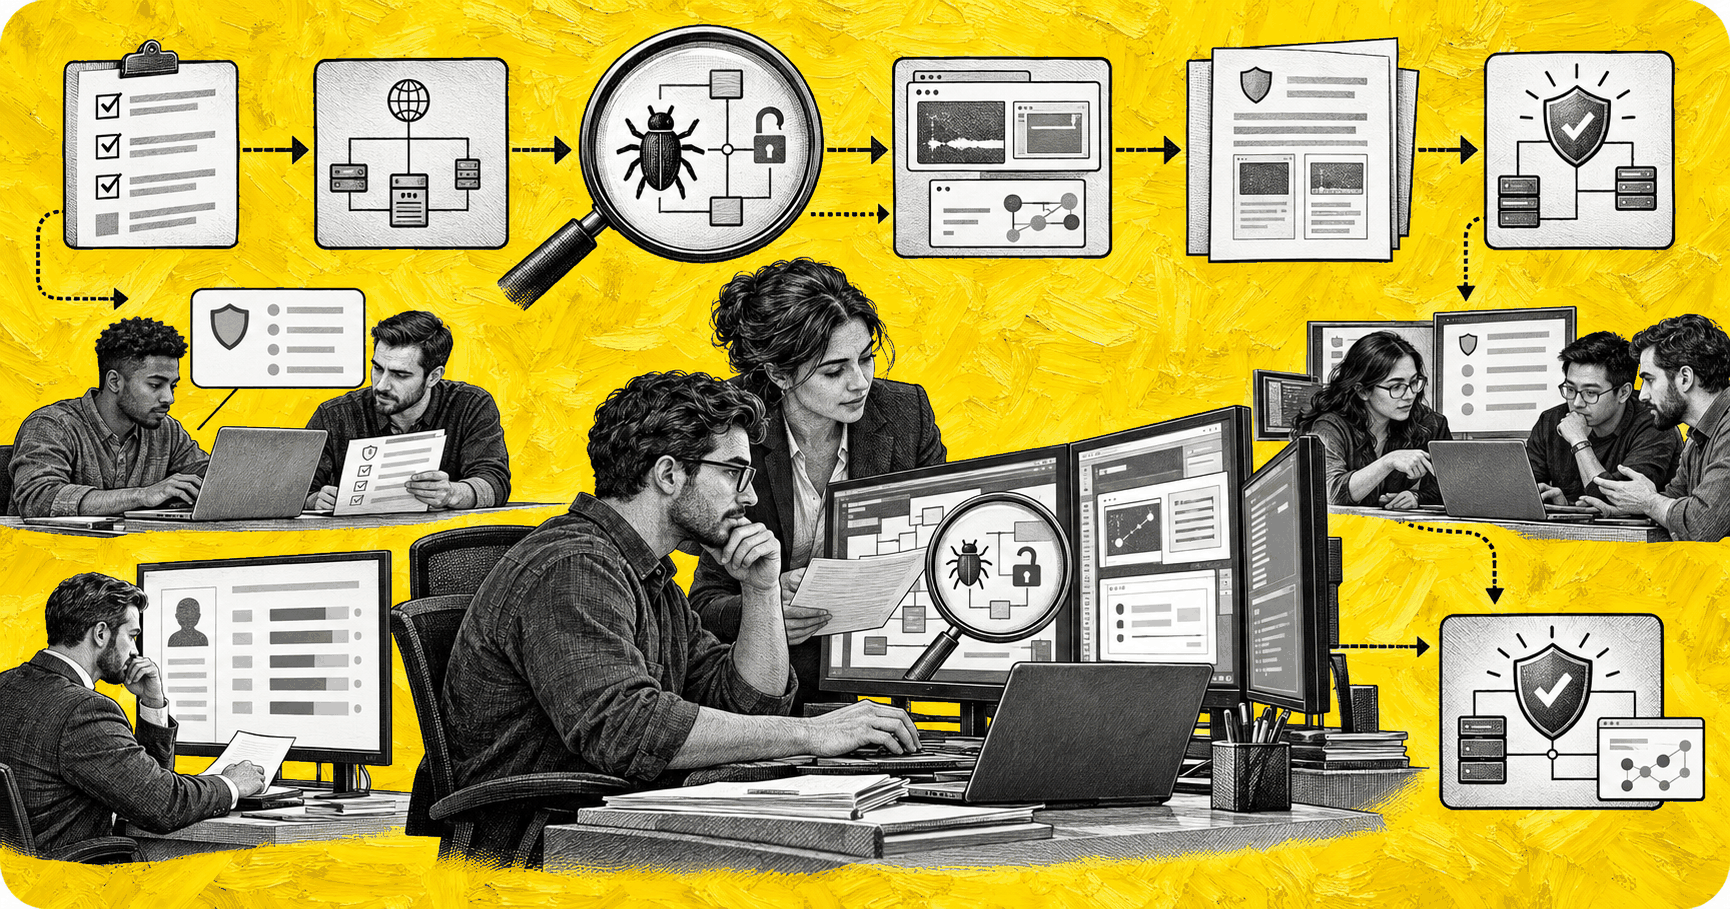
In practice, an in house bug hunter splits time between three kinds of work:
That last part separates a useful hire from someone who only collects findings, and your bug bounty hunter job description should say it outright.
The two roles overlap in skill but differ in shape. A penetration tester works inside a fixed scope and timeline, follows a methodology, and delivers a formal report at the end of an engagement. A bug bounty hunter works continuously, often across a wide and changing attack surface, and is judged on the impact and quality of individual findings.
Hire for bug bounty work when your attack surface changes often and you want ongoing coverage. Hire a penetration tester when you need scheduled, documented assessments for audits or compliance. If you want someone who can do both, say so plainly in the bug bounty hunter job description.
Copy this bug bounty hunter job description into your job posting and adjust the bracketed parts.
Job title: Bug Bounty Hunter (Security Researcher)
About the role
We’re looking for a bug bounty hunter to find and report vulnerabilities across [our web platform, mobile apps, and public APIs]. You’ll test our systems with full authorization, run our [internal / public] bug bounty program, and work with engineering teams to fix issues at the root. This is a [full time, remote / hybrid / onsite] role reporting to [Head of Application Security].
Responsibilities
Requirements
Nice to have
What we offer
[Salary range, benefits, learning budget, conference time, and any bonus tied to finding impact.]
A bug bounty hunter job description works best when it lists skills you can actually test. Group them so candidates can tell quickly whether they fit.
Degrees matter less here than in most technical roles, so weigh demonstrated findings over credentials.
A typical day starts with the report queue. The hunter reviews new submissions, reproduces the promising ones, closes duplicates, and asks researchers for missing details.
Midday is focused testing: mapping a newly launched feature, reading its JavaScript for hidden endpoints, and trying to break its authorization logic. Anything that works becomes a proof of concept and a short report.
The afternoon often goes to engineering partnership: walking a developer through a finding, checking a fix in staging, or proposing a shared library change that removes a class of bug. Some days include program work, such as updating scope after a launch.
Résumés are a poor signal for this role. Platform rankings can be inflated by low severity findings, and portfolios are hard to verify. The most reliable signal is watching a candidate find and explain a real vulnerability in a controlled environment.
Use this checklist to build your screening process:
Glider AI’s Bug Bounty Hunting Skill Test gives you a ready starting point for that hands on step. For candidates who also do structured testing work, pair it with the Penetration Testing Skill Test or the Ethical Hacker Skill Test.
Security roles attract some of the most capable people at gaming an online test, so integrity checks matter more here than almost anywhere else. Glider’s assessments include proctoring that candidates consent to step by step, watermarked questions that carry a unique candidate ID so leaked content can be traced, and code plagiarism checks. ID Verify matches photo ID, live selfie, location, and audio across the assessment and interview rounds, so a mismatch raises a flag before an offer, not after onboarding. Every flag is factual data for a recruiter to review, not an automatic rejection.
For the interview stage, the Bug Bounty Hunter Interview Questions page lists questions on hacking fundamentals and common vulnerability types. The full hiring process, from sourcing to offer, is covered in Hiring a Bug Bounty Hunter.
A bug bounty hunter finds security vulnerabilities in applications and systems, proves they can be exploited, and reports them with steps to reproduce and fix. In house hunters also triage reports from outside researchers and work with developers on remediation.
Include the systems in scope, core responsibilities (testing, reporting, triage, fix verification), the vulnerability classes you care about, required tools and scripting skills, expected experience, and how findings will be evaluated. The template above covers each of these.
Yes. “Bug hunter” is a common short form of bug bounty hunter. Both describe a security researcher who looks for vulnerabilities, usually under a bounty program or as an in house tester.
Strong web and API security knowledge, reconnaissance techniques, scripting in Python or JavaScript, experience with tools such as Burp Suite, and clear report writing. Judgment about scope and severity matters as much as technical skill.
Not usually. Many skilled hunters are self taught. Certifications such as OSCP or OSWE help show commitment, but a record of valid, well written findings is the stronger signal.
Use a hands on lab task in a controlled environment, score the written report alongside the finding, test scope judgment, and verify identity across rounds. A proctored skill test such as Glider’s Bug Bounty Hunting Skill Test covers the hands on step.
Start with the bug bounty hunter job description template above, then add a hands on assessment before the first interview. See how Glider AI helps security teams verify real skill and identity so only vetted candidates reach your hiring managers.
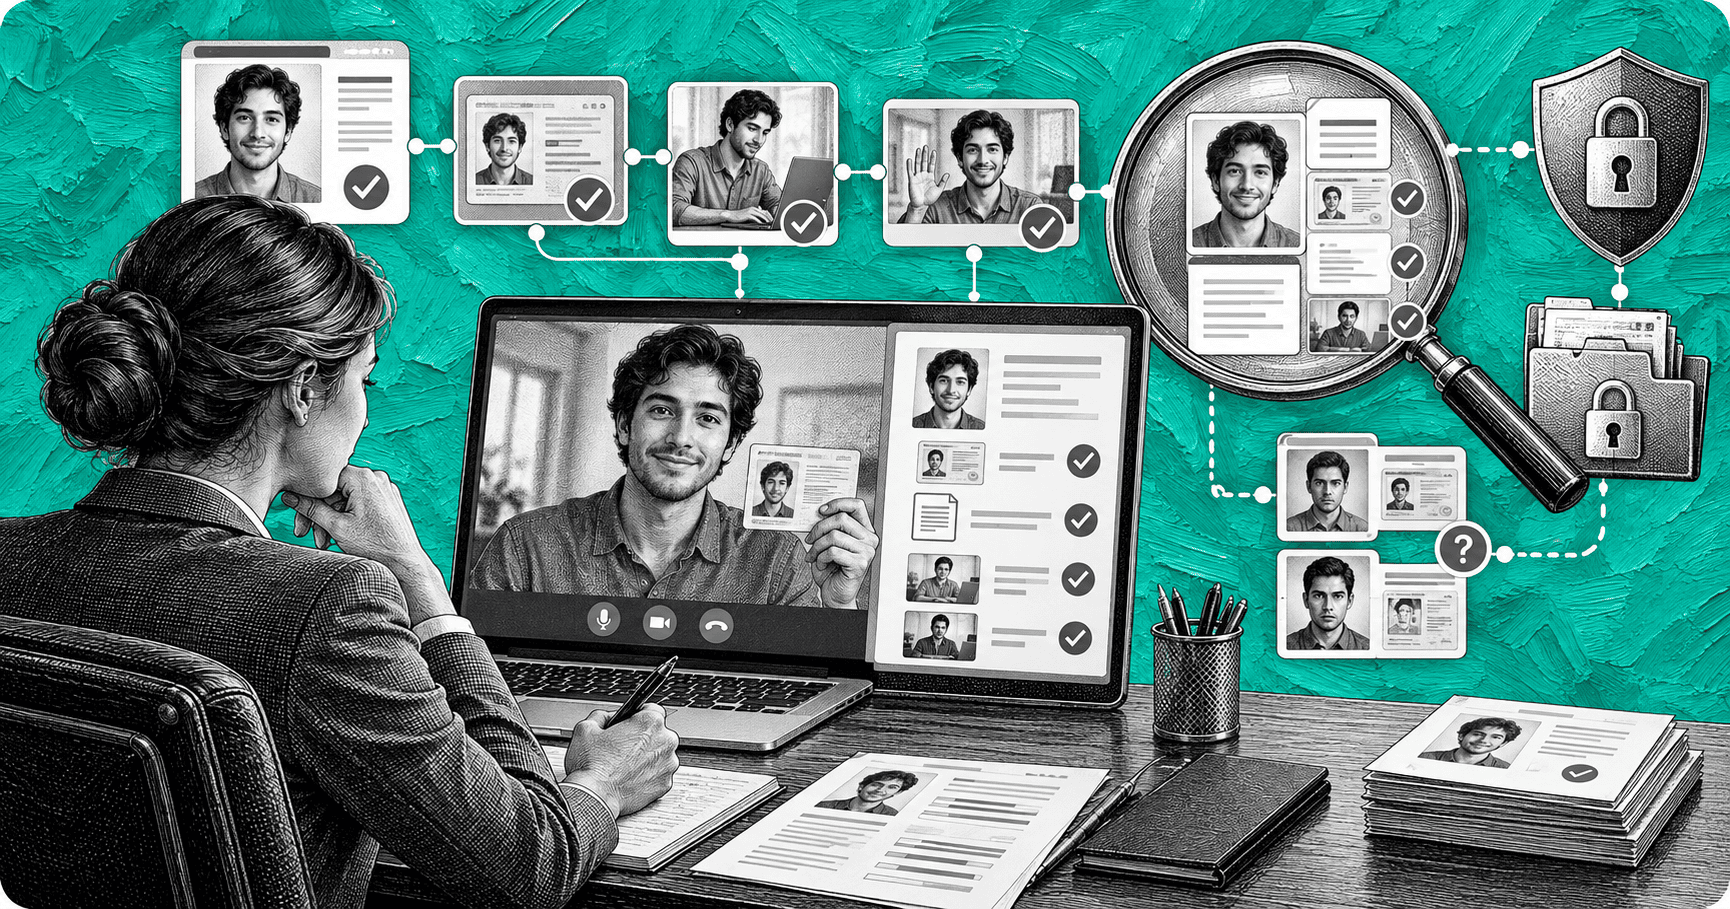
A recruiter screens a strong candidate on video, a hiring manager runs a solid technical round, and an offer goes out. On day one, the person who logs in is not the person who interviewed. Nobody on the team did anything careless. The process simply never confirmed who the candidate was. That gap is why […]
Introduction Technical roles are some of the hardest to fill. The process is a landmine of recruitment challenges. HR teams often find themselves under-resourced and struggling to find suitable talent, while engineers waste too much time interviewing candidates who don’t meet the necessary qualifications. Meanwhile, high-quality candidates get frustrated by slow and inefficient hiring processes and […]
What is QA and Testing? Quality Assurance (QA) and testing are integral processes in software development aimed at ensuring the reliability, functionality, and usability of applications. QA involves establishing standards and procedures to monitor and improve the software development lifecycle, focusing on preventing defects and identifying areas for optimization. It encompasses various activities such as […]
