

Make talent quality your leading analytic with skills-based hiring solution.
Hiring an ethical hacker means recruiting a security professional who is authorized to attack your own systems, find weaknesses, and report them before criminals do. The best way to hire one is to define the scope of the role, check for recognized certifications, and test real offensive skills with a hands on assessment instead of relying on resume claims.
This guide is for employers filling a full time or contract security role. It covers what the job involves, which skills and credentials matter, how to structure interviews, and how Glider AI Technical Assessments help security leaders see what a candidate can actually do before the first panel interview.
An ethical hacker, often titled penetration tester, offensive security engineer or red team operator, probes applications, networks and cloud environments with written permission. They think like an attacker, document every finding, and help engineering teams fix the root cause.
Typical responsibilities include:
The role sits between security operations and engineering. A strong hire is as useful in a design review as in a test window.
| Ethical hacker | Penetration tester | |
|---|---|---|
| Scope | Broad: any authorized offensive security work | Focused: time boxed tests against defined targets |
| Typical outputs | Red team campaigns, threat models, security research, test reports | Test reports with findings and remediation steps |
| Common titles | Offensive security engineer, red team operator | Pen tester, application security tester |
| Hiring focus | Creativity, attack chaining, communication with leadership | Methodology, tooling depth, report quality |
In practice many job descriptions use the terms interchangeably. Pick one title for the posting and describe the scope clearly so candidates self select.
Demand for offensive security skills outpaces supply, and resumes in this field are especially hard to read. Two candidates can list the same tools and certifications while having very different abilities to find and chain real vulnerabilities. Security managers also tend to run the technical interview themselves, so every unqualified candidate who reaches that stage costs senior time.
That is why the screening stage matters more here than in most roles. The goal is to move only candidates with demonstrated skill to the security team’s calendar. For a broader look at this problem, see our piece on challenges recruiters face in technical hiring.
Screen for skills you can observe, not just keywords you can match.
Certifications show commitment and a baseline of knowledge, but they are not proof of skill on their own. Common credentials hiring managers look for:
Treat certifications as one signal next to work samples, capture the flag history, disclosed vulnerabilities and a practical assessment.
A clear process keeps the security team focused on finalists.
Pay depends on experience, certifications, industry, clearance level and location. Regulated industries and roles that need a government clearance tend to pay more. Use current salary data from your compensation provider or recent offers in your market, and publish a range in the posting where local law requires it.
Glider AI gives security and TA teams a way to test offensive security skills before the interview loop starts. With Glider AI Technical Assessments, you can build role specific tests from a library covering 250+ technologies, mix question types, and add hands on simulations where candidates work through realistic tasks.
Every flag is evidence for a person to review, not an automatic rejection. Your security team still makes the call.
Written authorization. An ethical hacker works with permission from the system owner, follows a defined scope, and reports findings so they can be fixed. Employers bring them on as employees or vetted contractors. Unauthorized hacking services are illegal and are not what this guide covers.
Look for hands on experience with penetration testing, scripting ability, and one or more recognized certifications such as OSCP, CEH, CompTIA PenTest+ or GPEN. Disclosed vulnerabilities, capture the flag results and strong written reports are equally useful signals.
Use a practical assessment that asks candidates to find and explain vulnerabilities in a realistic environment. Score methodology, accuracy and reporting. Pair it with proctoring and identity checks so the results reflect the candidate’s own work.
OSCP is exam based and hands on, so many hiring managers treat it as stronger evidence of practical skill. CEH is widely recognized and useful for baseline knowledge. Neither replaces a skills assessment tailored to your environment.
It depends on seniority and market, but security roles often take longer than general engineering roles because qualified candidates are scarce. A structured process with an early skills assessment shortens the loop by keeping unqualified candidates off the security team’s calendar.
Full time hires make sense when you need continuous testing, threat modeling and close work with engineering. Contractors or firms suit periodic compliance tests. Many organizations use both.
Hiring an ethical hacker is a trust decision as much as a skills decision. Test the work, verify the person, and give your security leaders evidence they can review. See how Glider AI Technical Assessments help you screen offensive security candidates with hands on tests and proctored results, or explore the skill assessment overview to plan your next security hire.
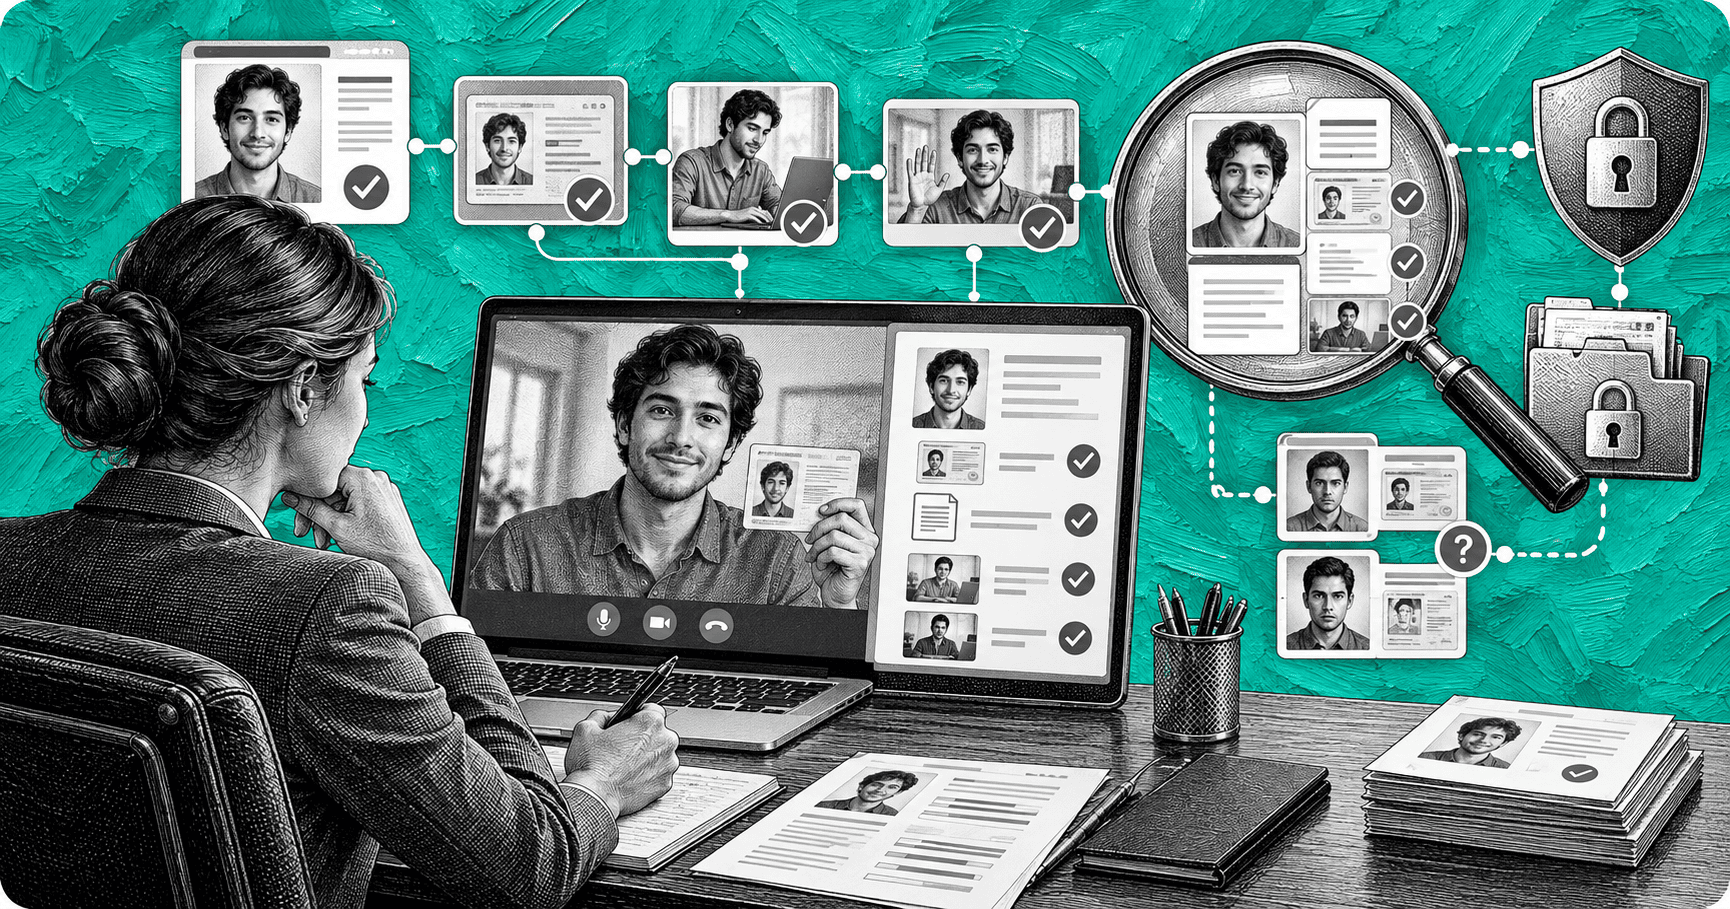
A recruiter screens a strong candidate on video, a hiring manager runs a solid technical round, and an offer goes out. On day one, the person who logs in is not the person who interviewed. Nobody on the team did anything careless. The process simply never confirmed who the candidate was. That gap is why […]
Introduction Technical roles are some of the hardest to fill. The process is a landmine of recruitment challenges. HR teams often find themselves under-resourced and struggling to find suitable talent, while engineers waste too much time interviewing candidates who don’t meet the necessary qualifications. Meanwhile, high-quality candidates get frustrated by slow and inefficient hiring processes and […]
What is QA and Testing? Quality Assurance (QA) and testing are integral processes in software development aimed at ensuring the reliability, functionality, and usability of applications. QA involves establishing standards and procedures to monitor and improve the software development lifecycle, focusing on preventing defects and identifying areas for optimization. It encompasses various activities such as […]
